North Face, Cartier Hit by Cyber Attacks: Customer Data Stolen - Bio Points News
North Face and Cartier report customer data stolen in recent cyber attacks. Hackers used credential stuffing at North Face, while Cartier’s systems were breached. No financial data was compromised.
North Face and Cartier Targeted in Latest Wave of Retail Cyber Attacks
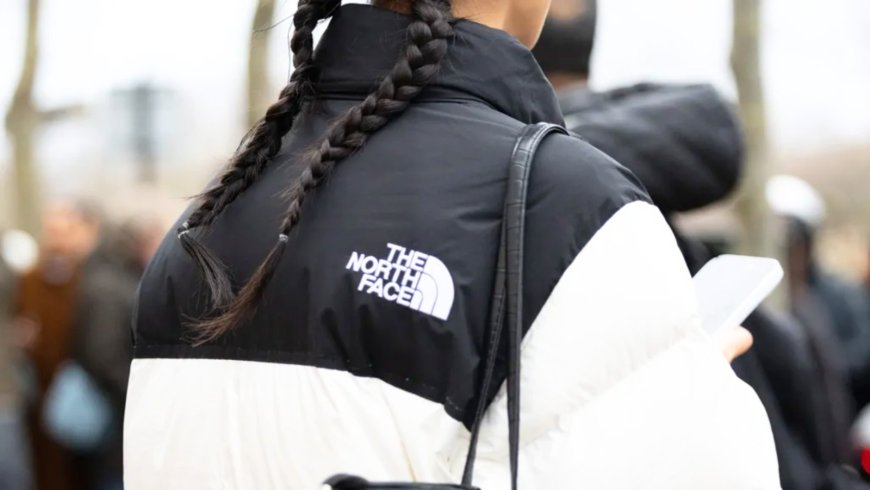
Fashion giants The North Face and Cartier have joined a growing list of retailers hit by cyberattacks, with customer data stolen in separate incidents. The breaches, part of a broader surge targeting high-profile brands, underscore the vulnerability of retail systems and the increasing sophistication of cybercriminals. The
North Face Faces Credential Stuffing Attack
A “Small-Scale” Breach with Big Implications
In April 2025, The North Face, owned by VF Corporation, detected “unusual activity” on its website, later identified as a “small-scale” credential stuffing attack. This technique involves hackers using usernames and passwords stolen from other data breaches, hoping customers reused them across accounts.
The attack compromised sensitive customer information, including:
-
Names and email addresses
-
Shipping addresses
-
Purchase histories
-
Dates of birth and phone numbers
North Face assured customers that payment card details remained secure. Affected users have been urged to change their passwords immediately to prevent further unauthorized access. The company notified customers via email and is working to bolster its cybersecurity measures.
This isn’t the first cyber hit for VF Corporation. In December 2023, a ransomware attack impacted its brand Vans, exposing personal data of approximately 35.5 million customers, underscoring ongoing vulnerabilities in the company’s systems.
Cartier’s Systems Breached
Limited Data Stolen, No Financial Impact
Luxury jeweler Cartier, owned by Richemont, informed customers on June 3, 2025, that an “unauthorized party gained temporary access” to its systems, stealing “limited client information.” The breach exposed names, email addresses, and countries of residence, but Cartier confirmed that passwords and financial details were not compromised.
“We contained the issue and have further enhanced the protection of our systems and data,” Cartier stated in an email to customers, adding that it has reported the incident to relevant authorities and is collaborating with leading cybersecurity experts to prevent future attacks.
Cartier warned that the stolen data could be used for targeted phishing attacks, urging customers to stay vigilant against suspicious communications. The company has not disclosed the exact date of the breach or the number of affected customers.
A Wave of Retail Cyber Attacks
Industry Under Siege
The North Face and Cartier breaches are part of a troubling trend targeting the retail sector. In recent weeks, brands like Marks & Spencer, Co-op, Harrods, Adidas, Dior, and Victoria’s Secret have reported similar incidents. Marks & Spencer, hit by a “highly sophisticated” attack in April, faces £300 million in lost profits, with online services disrupted until July. Victoria’s Secret temporarily shut its U.S. website in May due to a security incident, while Adidas reported stolen customer data from its help desk.
James Hadley, founder of cybersecurity firm Immersive, described retailers as “easy targets” due to their vast stores of customer data. “Retailers are overflowing with customer information,” he said. “Cyber-criminals are often content to play the long game,” using stolen data for social engineering scams to extract more sensitive information.
Credential Stuffing: A Persistent Threat
North Face’s breach highlights the growing menace of credential stuffing, where attackers exploit reused passwords. “This is not a new issue for The North Face’s parent company, VF Corporation,” noted Glenn Akester, Technology Director at Node4, pointing to the 2023 Vans attack. Customers are advised to use unique passwords and enable two-factor authentication to mitigate risks.
Authorities Respond, Customers Urged to Act
The UK’s National Crime Agency has prioritized catching the perpetrators behind these attacks, with the National Cyber Security Centre warning businesses to strengthen their defenses. “These incidents should act as a wake-up call,” a spokesperson said, emphasizing proactive cybersecurity measures.
North Face and Cartier are cooperating with authorities and have not yet responded to requests for further comment. Customers of both brands should remain cautious, updating passwords and monitoring for suspicious activity to protect their personal information.
A Call for Stronger Defenses
As cyber attacks continue to plague the retail industry, the North Face and Cartier breaches serve as a stark reminder of the risks posed by lax cybersecurity. With criminals exploiting vulnerabilities like credential stuffing and system hacks, retailers must invest in robust protections to safeguard customer trust. For now, affected customers are left to secure their accounts and stay vigilant in an increasingly digital world.
For more updates on cybersecurity and digital threats, visit Bio Points News.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0